
Intel Files Patent to Control Who Joins the AI Training Inside a 5G Network
Your carrier's 5G network is learning to run itself with AI, and Intel has filed a patent application on the guest list. It covers the digital passes that decide which parts of the network may join a shared AI training session.
What Intel's AI training pass for 5G does
Several computers inside a phone company's 5G network each sit on private data about how the network is holding up. None of them wants to hand that data over, but the company still wants one AI model that learns from all of it. The trick, called federated learning, has each computer train on its own data and send back only what it learned.
That raises a security question: who gets to join, and for which job? Today's permission system works like a building badge that opens every door once it checks out. Intel's patent application swaps in a pass tied to one specific training group and one specific type of analysis, so a computer cleared for one job can't be pulled into another.
For you, the payoff would be indirect: a network that can learn from its own performance and security data without that data being passed around loosely.
… finalize the FL group with the NWDAF MTLF (FL Client) selected from a list received from the NRF; request service from the NWDAF MTLF (FL Client); authenticate the NF service consumer and verify the access token; and provide an NF service response to the NF service consumer; and a memory to store the access token.
Translation: The system picks approved participants from a network registry to build the federated learning group.
How the 5G core hands out and checks tokens
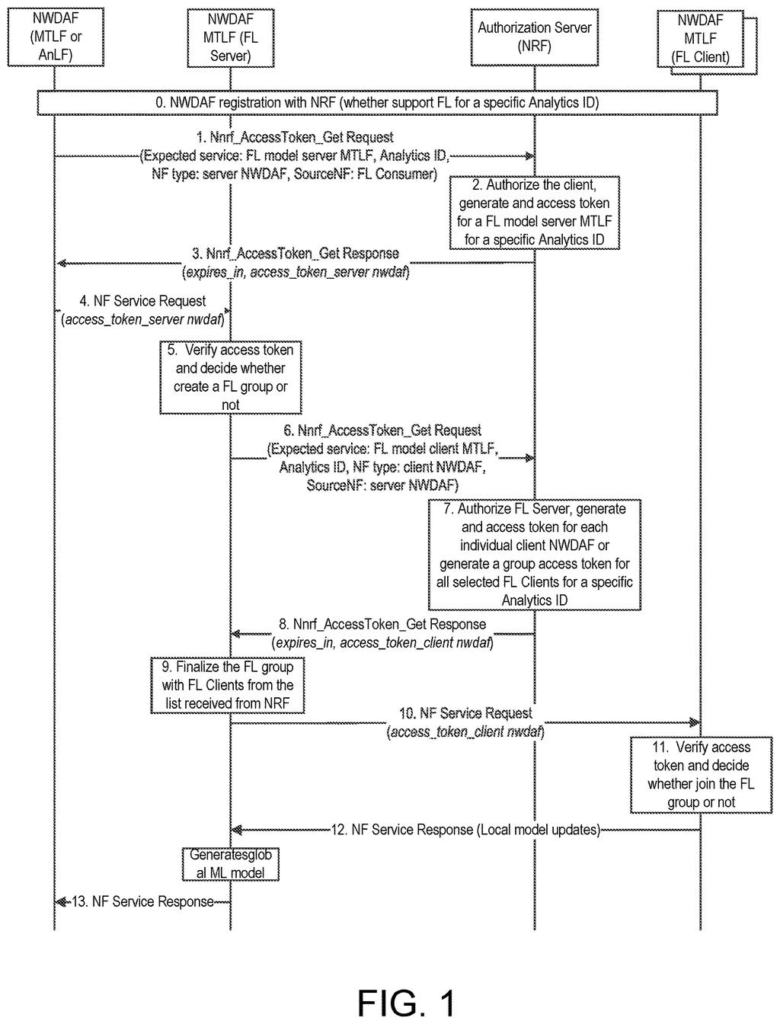
The patent covers a handshake inside the part of the 5G core that analyzes network data (called the NWDAF, short for network data analytics function). One analytics unit acts as the FL server, which coordinates the training. Others act as FL clients, which train locally on data they never share.
The claims describe this flow:
- Another analytics unit asks for an access token to use the server's training services, and the server validates it.
- The server asks the network's directory, the NF repository function (NRF), for a second token. The request names the target client, the type of analysis (the Analytics ID), the FL group ID and a credential proving who asked.
- The server finalizes the group from the list of clients the NRF returns, then requests service from them.
- Each client authenticates the requester and checks the token, including the server's identity, group ID, Analytics ID and model ID.
- The server sends a response back to the requester. The description adds that it combines the clients' local updates into a global model.
The NRF only issues a token when the server or client really supports federated learning for that type of analysis, and optionally has enough computing capacity. The filing describes either one shared token for the whole group or one token per member. It also lets servers and clients cap the share of computing power each group can use.
The device may send a request to get an NF repository function (NRF) access token from an NRF. The device may perform global model updates and aggregation. The device may provide an NF service response to the NF service consumer.
Translation: The server gathers updates from participating nodes to train the shared AI model.
Why finer permissions matter for 5G network AI
Phone networks increasingly use AI to watch traffic, spot faults and flag security threats. When several of those AI units must train together, a loose permission system could let the wrong unit into the wrong job. Group-level passes let a unit say yes to one task without opening everything it can do.
The patent office has approved this application, and once Intel pays the final fee it should be issued as a granted patent. The filing ties back to standards work at 3GPP (the body that writes mobile network rules), where Intel's description says security teams were studying exactly this gap. The audience is carriers and network equipment makers, so you would never see this on your phone screen.
Intel's fifth filing we've tracked since July on on-device AI privacy, building on work on scrubbing factory speech and blocking a PC's own wake-word triggers, pushes further toward keeping audio private on the device.
You will almost never notice this one. It sits deep inside a carrier's network, and the only sign it works is that nothing goes wrong.
The failure it prevents is a mix-up over who may help train the AI that watches your carrier's network. A pass that names one group and one job keeps a helper from wandering into work it was never cleared for.
Verdict: routine security plumbing, and sensible plumbing at that. Most readers get no direct benefit, but carriers have good reason to lock down AI that touches private network data.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Intel patent news breaks.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings
6 drawing sheets from US 2026/0333048 A1 · click any drawing to enlarge


Want this weekly breakdown for a company we don't cover? Patentlyze Pro →
Be the first to weigh in