
Samsung
Samsung · Security · Filed Apr 1, 2026 · USPTO published Aug 6, 2026 · Aug 6 release
Samsung Patents a Dual-Vault System for Managing Data Encryption Keys
Samsung is patenting a system where a device encrypts its own encryption key twice over, sending it to two completely separate security systems and storing the results independently. If one vault is compromised, your data still isn't.
- Publication number
- US 2026/0230304 A1(US20260230304A1)
- Applicant
- Samsung Electronics Co., Ltd.
- Filed · Published
- Apr 1, 2026 · Aug 6, 2026
- Inventors
- Jongwon KIM, Dongyeol KIM, Taehyeong LEE, Jinsoo KANG, Seungchul KO, Eunsoo PARK, Seunggyu BAEK, Yeonseong HWANG
- Status when we published
- Waiting for an examiner
- Document
- 16 claims
- US classification
- 713/168
- Parent application
- Continuation of PCT/KR2024/011611 (filed Aug 6, 2024)(PCTKR2024011611)
What Samsung's double-encrypted key system actually does
Imagine you write a diary and lock it with a key. Then, instead of just hiding that key under a rock, you make two copies of it, give each copy to a different trusted friend, and each friend puts their copy in their own separate safe. Even if someone breaks into one friend's safe, they still can't get into yours.
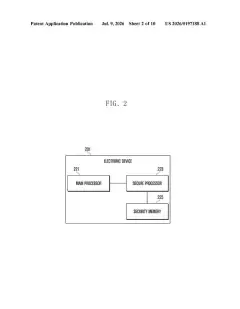
That's roughly what Samsung is patenting here. A device generates a key that scrambles its data. It then sends that key to two different security systems, each of which wraps it in their own separate lock before sending it back. The device stores both locked versions, each labeled with enough information to know which security system holds the matching key.
The practical result is that no single point of failure can expose your underlying data. If one security system is unavailable or breached, the other can still be used to recover access. It's a redundancy-plus-resilience approach to a problem that's become very real for enterprises managing sensitive data across cloud environments.
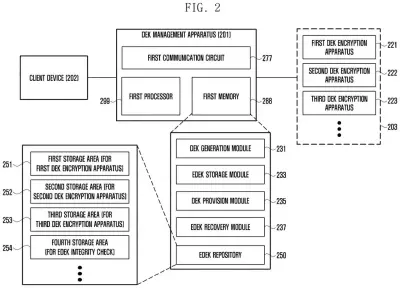
generate a data encryption key (DEK), transmit a first DEK encryption request message including the DEK to a first DEK encryption apparatus through the communication circuit, transmit a second DEK encryption request message including the DEK to a second DEK encryption apparatus through the communication circuit …
Translation: The device creates a security key and sends it to two separate external systems to be encrypted for safekeeping.
How the DEK gets wrapped by two independent KEKs
The patent describes an electronic device that acts as a coordinator between two independent key encryption key (KEK) systems. A KEK is essentially a lock for your lock: rather than store a raw encryption key on a device (where it could be stolen), you encrypt that key with a second key held by a separate, trusted system.
Here's the step-by-step flow the patent outlines:
- The device generates a data encryption key (DEK), which is the key that actually scrambles stored data.
- It sends the DEK simultaneously to two separate DEK encryption apparatuses (think: two different key management servers or hardware security modules).
- Each system encrypts the DEK with its own KEK and returns an encrypted DEK (EDEK) plus an identifier for the KEK it used.
- The device stores each EDEK in its own dedicated memory partition, tagged with the DEK's identifier and the corresponding KEK identifier.
The key insight is that the raw DEK is never stored anywhere. Only the two encrypted versions are kept, each tied to a different external system. To access data later, the device can reach out to either system, present the correct EDEK, and get the original DEK back. The dual-storage design means the system can tolerate one key management server going offline or being unavailable without losing access to the underlying data.
… store the first EDEK, identification information of the DEK, and the identification information of the first KEK in a first storage area of memory corresponding to the first DEK encryption apparatus, and store the second EDEK, the identification information of the DEK, and the identification information of the second KEK in a second storage area …
Translation: The system saves the encrypted keys and their tracking data into two distinct memory locations for redundancy.
What this means for enterprise and device data protection
For everyday consumers, this is background infrastructure, but for enterprise and cloud deployments, it addresses a real operational headache. Companies often use hardware security modules or cloud key management services to protect encryption keys, but relying on a single provider creates a single point of failure. Samsung's approach builds redundancy directly into the device, so data stays accessible even if one key management backend has an outage or is taken offline for maintenance.
This kind of architecture is increasingly relevant as regulations in healthcare, finance, and government require both strong encryption and demonstrable recovery capabilities. A device that can prove it stores encrypted keys across two independent systems makes compliance audits considerably cleaner.
Source: US 2026/0230304 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Samsung patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 7 sheets
7 drawing sheets from US 2026/0230304 A1 · click any drawing to enlarge


More from Samsung
All 1,629 Samsung patents →
More in Security
All 341 Security patents →
IBM
IBM Patents a System That Builds Encryption Keys From Your Message History
Nvidia
Nvidia Patents a Write-Only Memory System for Cluster Encryption Keys
AMD
AMD Patents a Circuit That Locks GPU Memory Behind Per-Request Encryption Keys
Sony