
Microsoft Files Patent to Let Security Teams Search Many Databases by Just Asking
Hunting for ransomware today can mean learning a different query language for every database. Microsoft's filing describes a search that reads your plain-English question, picks the right databases, and writes the queries itself.
What Microsoft's ask-anything security search does
You're a security analyst and a client just told you ransomware might be loose on their network. Their clues are scattered across incident lists, device records, and logs, each stored differently and each needing its own special query language. Before you can answer anything, you have to learn where to look and how to ask.
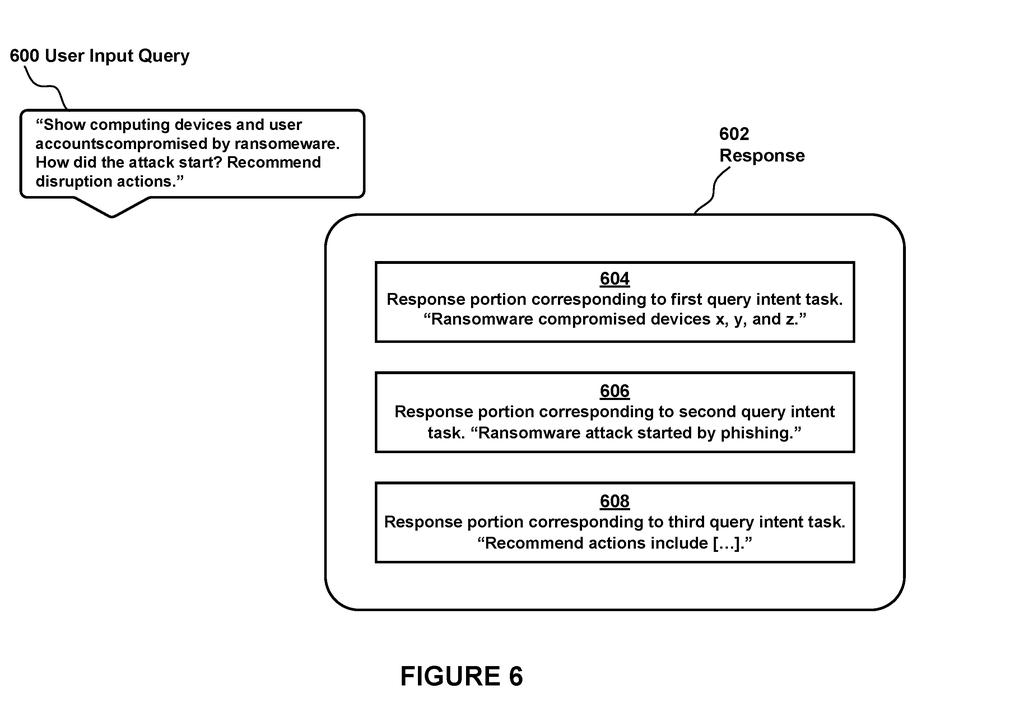
This Microsoft filing describes a way to skip that. You type a normal sentence, like 'show me the computers and accounts hit by ransomware, and how it started.' The system first builds a map of how all the data sources connect. Then it figures out what you're really after, breaks your question into smaller pieces, and sends each piece to a helper program built to search one kind of data.
The helpers can pass findings to each other, and an AI language model stitches the results into one answer you can read.
mapping a query intent to a relevant data source according to a data map representation to identify a query intent task, wherein entities and context associated with an input query used to determine the query intent …
Translation: Translating a plain question into the right database by using a map of how different data sources relate to each other.
How a map of your data picks which agent to send
Every claim in the filing centers on one pipeline. A query intent (a guess at why someone asked) is mapped to the right data source using a data map representation (a graph showing how databases, tables and columns relate). The task then runs on a search agent that is parameterized for that source, meaning it is configured to speak that source's language, such as Kusto Query Language or Cypher.
- Build the map: the system writes descriptions and metadata for each source, turns them into embeddings (number fingerprints of meaning), and uses a language model to label links like shared fields or similar content.
- Read the question: it picks out entities (devices, accounts, ransomware) and context (words like 'list' and 'compromised by'), then splits a big question into sub-intents.
- Route and run: each sub-intent goes to a matching agent. Agents can hand output to one another, and the results are combined.
This differs from the usual retrieval-augmented generation (RAG, where an AI looks up similar text and pastes it into a prompt). Here the question's embedding is only a starting point on the map, which the system keeps exploring, for example to find how two tables could be joined. Adding a new source means updating the map and adding an agent for it.
A natural language search enables searching across available data sources, independent of underlying storage architectures or query languages.
Translation: You can query multiple different database types using plain English without needing to know their specific search languages.
What this means for analysts stuck writing queries
If you work in security, the daily grind includes digging through logs and incident records spread across different systems, each with its own query language. A tool built on this filing would let you ask in plain English and get one answer covering several sources. The filing's own example response lists infected devices, how the attack began, and recommended steps like isolating machines.
The filing says the same approach could apply well beyond security, to areas like healthcare, finance or logistics, anywhere data sits in mismatched systems. The appeal is that a new source only needs a map entry and an agent, with little extra computing. The filing names no product, though.
Microsoft's 23rd filing we've tracked since July in our AI agents that work for you watch adds to earlier applications like the fewest-steps planner and the screen-watching bug finder.
Nothing here needs new hardware. It is all software layered on top of language models and databases a company already runs, so the distance to a working feature is short on paper. The shortest route is a security tool that starts with two or three data types, such as Kusto tables, SQL and graph databases, each with its own agent.
What has to exist first is the map, and the filing says it should be built automatically with no human involvement. That is the step most likely to cause trouble, because a wrong link between two tables sends every later search the wrong way. The document gives no accuracy numbers or test results, only a worked ransomware scenario.
Our read: a practical idea with a believable path to a product. The hard work lies in checking the answers, and a patent filing does not cover that.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings
10 drawing sheets from US 2026/0332628 A1 · click any drawing to enlarge


Show the other 2 sheets


Want this weekly breakdown for a company we don't cover? Patentlyze Pro →
Be the first to weigh in