
Google Patents a Secure Space That Puts Users in Control of Online Ads
Every time a web page loads an ad, your browser fires off a request packed with data about you and your device. Google has patented a system that puts a locked box around that process, giving the browser itself more control over what gets sent and to whom.
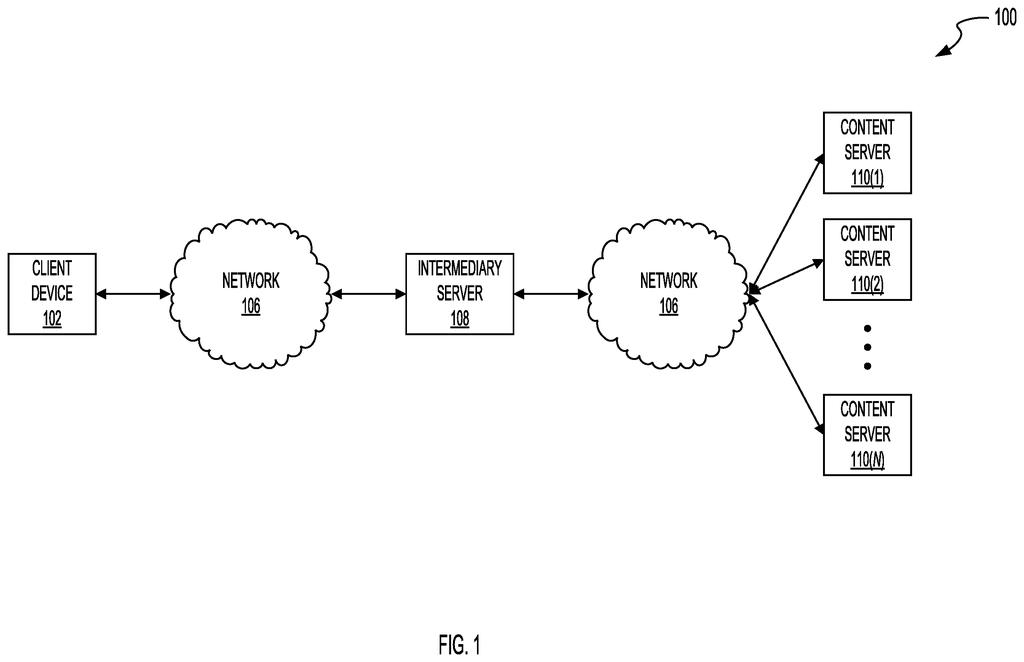
How Google's browser sandbox keeps ad data local
Today, when a website loads an ad, your browser typically sends a detailed request to an ad server, often including information about your device, your browsing context, and more. That data travels outward with very little gatekeeping at the browser level. Google's patent describes a different setup.
The idea is to run ad-request code inside a restricted environment, essentially a walled-off zone inside your browser that the browser itself controls. Your device stores a profile of its own parameters, and when a page loads, the browser feeds that profile into the restricted zone. The zone assembles a list of parameters and passes it to a go-between server, which only sends an ad back if the data meets certain thresholds.
The result is that your raw device data never has to travel directly to the ad server. The browser acts as a checkpoint, not just a messenger. That's a meaningful shift from how ad tech works today.
Systems and methods described herein can provide a restricted environment for the local execution of server provided processor-executable instructions.
Translation: Google's system runs server code locally inside a protected browser sandbox.
Inside the restricted environment and proxy handoff
The patent describes a method with several distinct moving parts.
First, your browser stores a client device profile, a collection of parameters describing your device and potentially your preferences, alongside executable code that knows how to assemble ad requests. That code lives inside a restricted environment (think of it like a sandbox: code running in there can't reach outside without permission) tied to a specific content server.
When you load a web page with an ad slot, the browser passes a content item parameter (context about the ad placement) into the restricted zone. The sandboxed code then combines that with the device profile to build a parameter list.
Instead of sending that list directly to the ad server, the browser sends it to a proxy server. The proxy checks whether an aggregate value of those parameters clears a predetermined threshold before returning an actual ad. That threshold check is the privacy gate: it may prevent any single data point from being individually identifying.
- Device profile and ad-request code stored locally in a restricted zone
- Browser controls what enters and exits the sandbox
- Proxy server applies threshold logic before returning content
- Ad server never receives raw, unmediated device data
… generating, by the web browser executing the processor-executable instructions stored in the restricted environment, a parameter list based on the client device profile and the content item parameter; …
Translation: The browser uses device data to build an ad tracking list right on your phone.
What this means for your data when ads load
If this system shipped, the most direct thing you'd notice is nothing, and that's the point. Ads would still load, but the path your device data takes to get them there would change. Your browser would act as a filter rather than a transparent pipe, and some data that currently travels to ad servers might never leave your device at all.
For Google's track record in privacy-architecture patents, this fits a pattern of re-engineering ad delivery to survive a world where third-party cookies are disappearing and regulators are paying closer attention. The proxy and threshold design could help Google argue that ad targeting happens without direct exposure of individual user data, which matters a lot in ongoing conversations about privacy law in the US and Europe.
Google's 52nd filing we've tracked since May builds on earlier applications covering showing crowd levels privately and on-phone AI memory limits, all part of the on-device AI privacy push.
Your browser handles a quiet negotiation every time a page loads, and this patent describes what happens on your side of that negotiation. Instead of sending your individual browsing behavior straight to an ad company's servers, your device does the matching work locally, inside a contained section of the browser you never see or interact with.
The practical result is that an ad company learns something about a broad group of people you happen to resemble, rather than a detailed record of what you specifically clicked, searched, or read this week. You would notice this failing only if it broke, which is the point: the whole design is meant to make a privacy problem invisible by preventing it.
The open question for any user is who writes the rules for that contained space. The browser maker sets the boundaries, so the protection is real but rests on that company's choices holding firm over time.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings
5 drawing sheets from US 2026/0289015 A1 · click any drawing to enlarge


Want this weekly breakdown for a company we don't cover? Patentlyze Pro →
Be the first to weigh in