

Microsoft
Microsoft · Security · Filed Dec 3, 2024 · USPTO published Jun 4, 2026 · Jun 4 release
Microsoft's New Patent Wants to Connect Every Known Hacker, Malware, and Attack Into One AI-Readable Map
Imagine every known hacker group, malware strain, and attack technique connected in a single web — and an AI that can read that web and explain what any one node means in plain English. That's essentially what Microsoft is building here.
- Publication number
- US 2026/0154316 A1(US20260154316A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Dec 3, 2024 · Jun 4, 2026
- Inventors
- Michael Charles ALBADA, Anush SANKARAN, Amir Hossein ABDI, Tong WANG
- Status when we published
- Waiting for an examiner
- Document
- 20 claims
- US classification
- 704/9
- Examiner
- PASHA, ATHAR N (Art Unit 2657)
What Microsoft's threat intelligence graph actually does
Picture your security team getting hit with hundreds of threat reports every week — PDFs, blog posts, advisories about ransomware gangs, zero-days, and suspicious IP addresses. Reading all of it is impossible. Connecting the dots between, say, a new malware family and the nation-state group that typically deploys it is even harder.
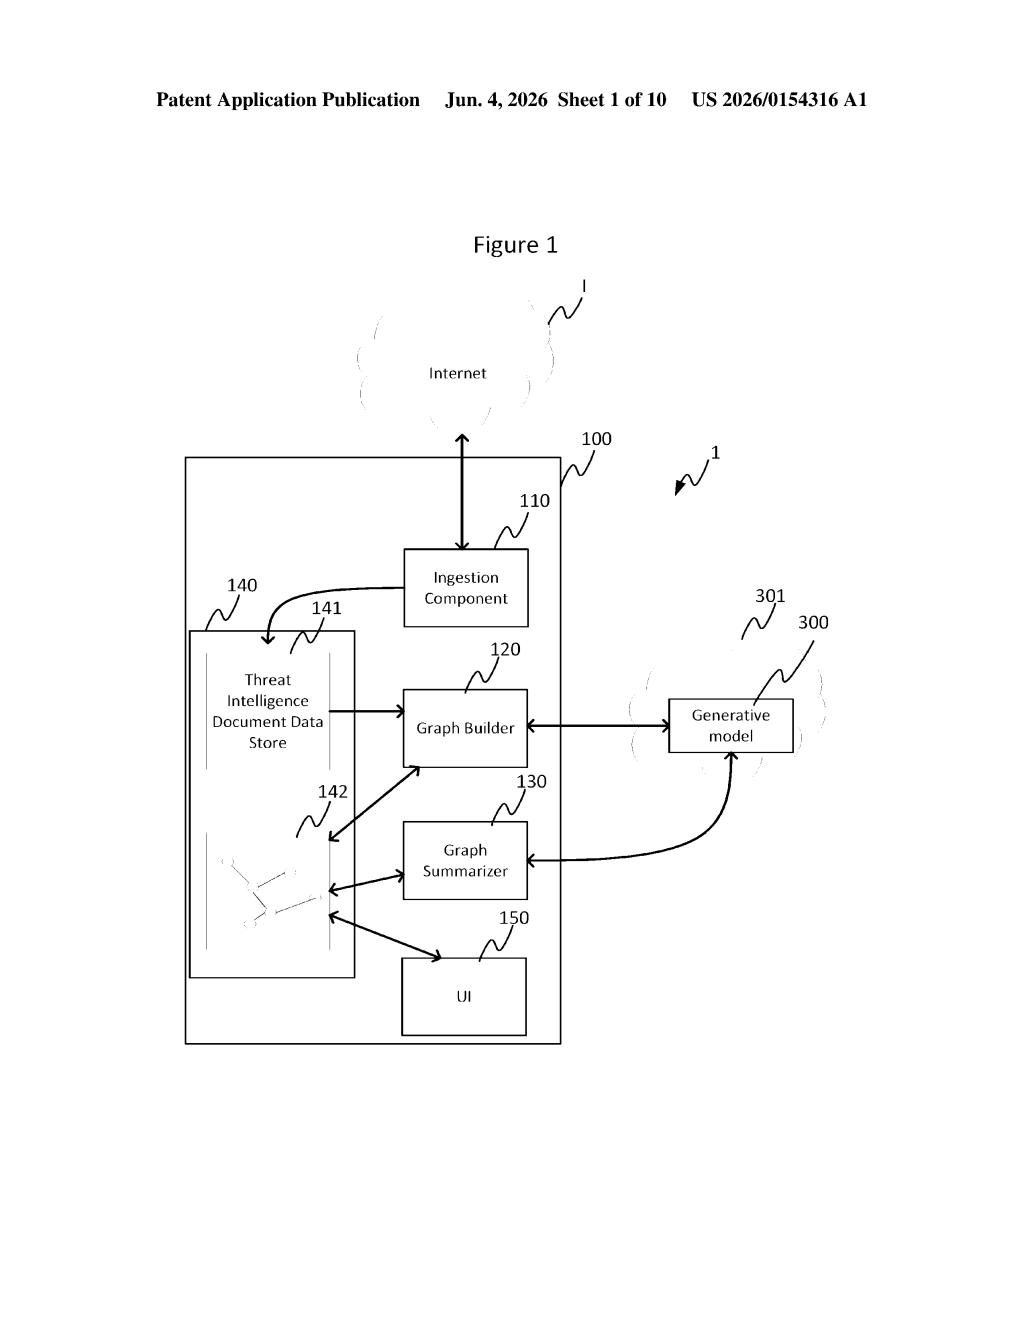
Microsoft's patent describes a system that ingests all those threat documents and automatically builds a knowledge graph — a web of connected entities like hackers, malware, and vulnerabilities, with lines showing how they relate to each other. Every connection traces back to the source document it came from, so nothing is made up.
Here's the clever part: when you want to understand a specific threat actor or piece of malware, the system feeds that node plus all its connected neighbors into an AI model, which writes a plain-English summary grounded in the actual source documents. That summary then gets added back into the graph as its own node, making future lookups even richer.
How the LLM reads the graph and writes threat summaries
The system works in two broad stages: graph construction and AI-driven summarization.
In the first stage, threat intelligence documents — think vendor reports, CVE advisories, OSINT feeds — are parsed to extract entity nodes (malware names, threat actor groups, IP addresses, attack techniques, vulnerabilities) and edges (the relationships between them, like "group X uses malware Y" or "vulnerability Z is exploited in campaign W"). Critically, every node and edge retains a pointer back to the specific source document it came from, preserving provenance (a trail of evidence you can audit).
In the second stage, when a summary is needed for a target entity, the system assembles a prompt for a generative ML model (think a large language model, or LLM) that includes:
- The target entity node itself
- All directly connected neighbor nodes
- The original source documents those nodes and edges came from
- Instructions telling the model to produce a threat-intelligence summary grounded in those sources
The LLM's output — the summary text — is then written back into the graph as a new summary node, with edges connecting it to all the entities it describes. This means summaries become first-class citizens in the graph and can inform future queries, not just one-off outputs.
What this means for security analysts drowning in threat data
Security analysts spend an enormous amount of time on what's sometimes called threat hunting triage — figuring out whether a new indicator of compromise is connected to something they've already seen. A structured knowledge graph with AI-generated summaries could compress hours of cross-referencing into seconds, and because every claim traces back to a source document, analysts can verify rather than just trust the output.
For Microsoft specifically, this fits neatly into the Microsoft Sentinel and Microsoft Defender Threat Intelligence product lines, both of which already ingest external threat feeds. Baking an LLM-powered graph layer into those products would give enterprise security teams a meaningfully faster path from raw threat data to actionable context.
Source: US 2026/0154316 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
More from Microsoft
All 646 Microsoft patents →


More in Security
All 341 Security patents →
AMD
AMD Patents an AI Malware Detector That Runs Outside Your Main Processor

IBM
IBM's New Patent Moves Malware Scanning Off the Main Server to a Dedicated Device

Microsoft
Microsoft Patents an AI System That Reads Security Logs and Summarizes Threats Automatically

Samsung