
Microsoft
Microsoft · Security · Filed Jan 30, 2026 · USPTO published Jun 18, 2026 · Jun 18 release
Microsoft's New Patent Stops Corporate Security from Forgetting a Repaired Device
Every time a technician swaps a motherboard or replaces a hard drive, the device can look like a completely different machine to corporate security systems. Microsoft's new patent tries to fix that automatically.
- Publication number
- US 2026/0170182 A1(US20260170182A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Jan 30, 2026 · Jun 18, 2026
- Inventors
- Brian Stuart PERLMAN, Daniel Chavez ZAYAS, Eric Phuoc HUANG, Marilyn Lai SUN, Hung Minh DANG, Juanita Jestina BAPTISTE, Zakariyah Toyer
- Status when we published
- Waiting for an examiner
- Document
- 20 claims
- US classification
- 726/26
- Parent application
- Continuation of 17/828,876 (filed May 31, 2022)(17828876)
What Microsoft's post-repair device identity fix actually does
Imagine your work laptop goes in for a repair — the technician replaces the motherboard. When it comes back, your company's IT security system sees what looks like a brand-new, unregistered device. That can lock you out of corporate tools, trigger security alerts, or force your IT department into hours of manual re-enrollment work.
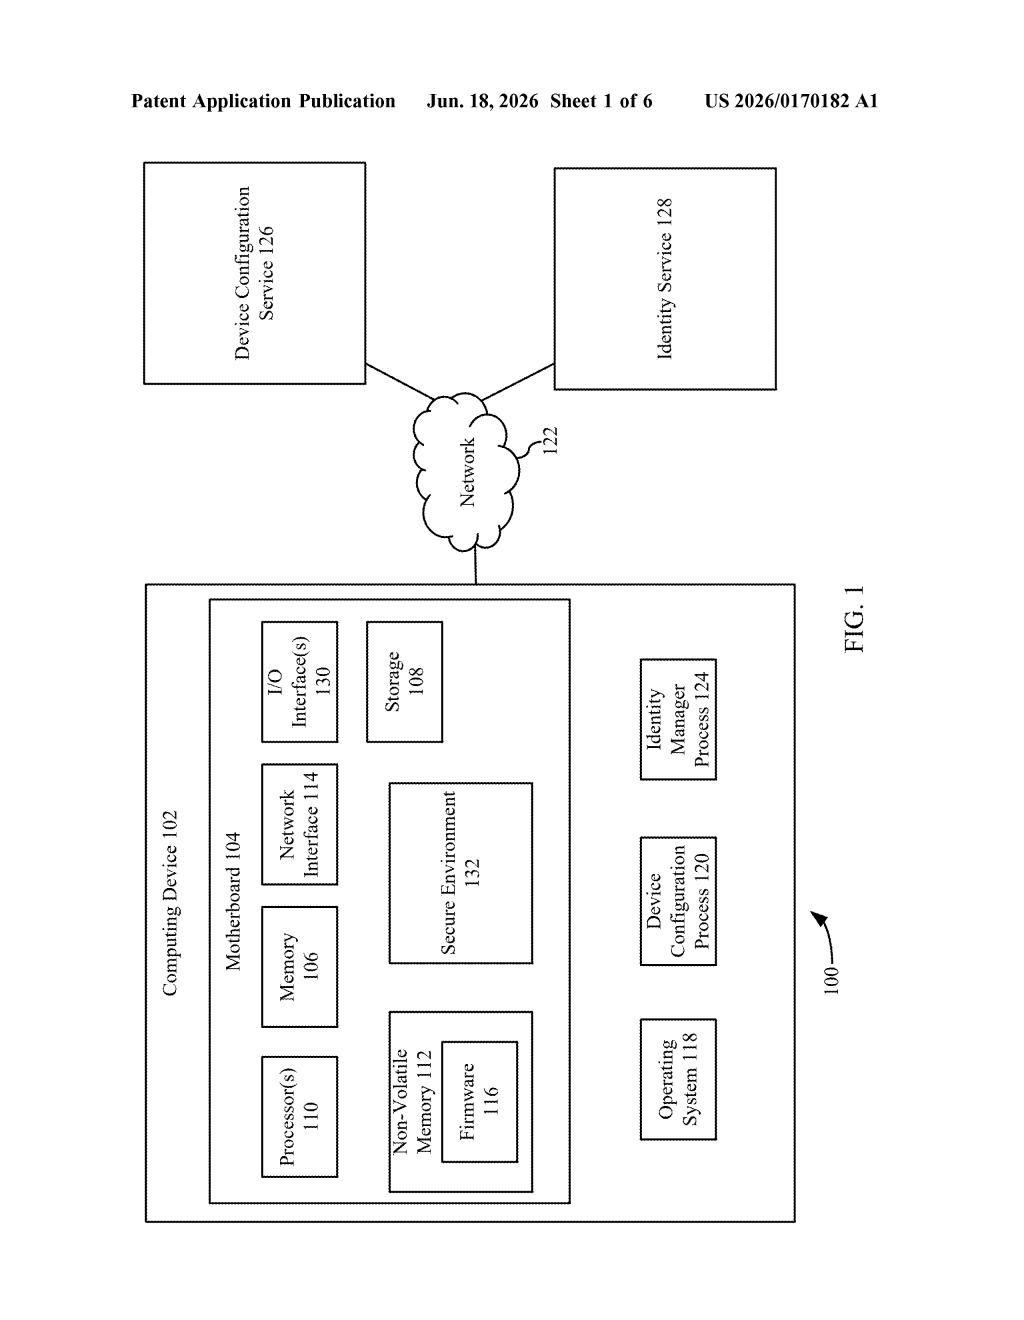
Microsoft's patent describes a system designed to handle this automatically. When your device is first set up, it gets a unique ID marker baked in — one that survives even a full Windows reinstall. The device periodically takes a kind of "hardware snapshot" and compares it against a stored version. If the hardware changes (say, after a repair), it flags the mismatch and notifies a cloud service.
That cloud service then securely re-registers the repaired device under its original identity, so your IT department doesn't have to intervene. The system also cleans up any conflicting records in the device database, keeping everything tidy on the back end.
How the fingerprint comparison and cloud re-registration works
The patent describes a cloud-backed system that tracks a device's hardware fingerprint — essentially a unique profile built from the physical components inside the machine (processor, storage, network card, etc.). This fingerprint is taken at regular intervals and stored both locally and in a remote service.
At first setup, the device also generates a GUID (Globally Unique Identifier — think of it as a serial number that can't be wiped by reinstalling the operating system). This GUID acts as a persistent anchor: even if every piece of hardware gets replaced, the GUID provides a thread back to the device's original registered identity.
When the periodic check detects that the current hardware fingerprint doesn't match the stored one — a sign that components have changed — the device sends a request to a cloud service. That service holds the original identity data and uses the GUID as a hint to confirm it's dealing with the same device.
The cloud service then performs a secure re-registration: it transmits the updated identity back to the device over an encrypted channel and resolves any conflicts in the device management records (so the repaired machine doesn't appear twice in the system, for example). The whole flow is designed to run without requiring manual IT intervention.
What this means for corporate IT and device management
For corporate IT departments managing thousands of devices, hardware repairs are a persistent headache. A repaired laptop that loses its registered identity can fall out of compliance tracking, lose access to corporate resources, or trigger false-positive security alerts — all of which take time and money to fix manually. Microsoft's system, if it ships, would automate that recovery process entirely.
This also matters for security policy. The patent is classified under hardware identity verification (USPC 726/26), placing it squarely in the access-control space. A system that can reliably confirm "this is the same device, just repaired" — rather than an unknown machine — is a meaningful improvement for zero-trust security models, where every device is treated as potentially hostile until verified.
Source: US 2026/0170182 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
More from Microsoft
All 646 Microsoft patents →


More in Security
All 341 Security patents →
IBM
IBM Patents AI That Scores Online Identity Checks Before Granting Access

AMD
ATI Technologies Patents a Hardware System That Keeps Streaming Rights Locked Inside the Chip

Amazon
Amazon Patents a Way to Track the Original Identity Behind Assumed AWS Roles
Microsoft