
Microsoft
Microsoft · Security · Filed Mar 28, 2025 · USPTO published Oct 1, 2026 · Oct 1 release
Microsoft Patents a Three-AI System That Assigns and Monitors Its Own Security Fixes
When a cyberattack hits a corporate network, the clock starts ticking. Microsoft's new patent describes a trio of AI agents that, without waiting for a human to notice, picks the best responder, writes the fix, and watches to make sure it actually works.
- Publication number
- US 2026/0303618 A1(US20260303618A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Mar 28, 2025 · Oct 1, 2026
- Inventors
- Maor NISSAN, Roee OZ, Tamer SALMAN, Andrey KARPOVSKY, Fady COPTY, Tamara GAIDAR
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 726/22
- Examiner
- KNACKSTEDT, JACOB BENEDICT (Art Unit 2408)
How Microsoft's AI security responders divide up the work
Every time a suspicious login or strange data transfer shows up on a corporate network, someone has to decide who handles it, what exactly they should do, and whether it worked. Right now, that chain of decisions usually runs through a human security analyst, and analysts are expensive, overloaded, and unavailable at 3 a.m.
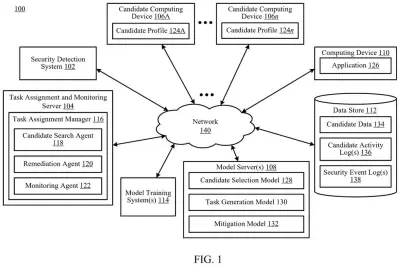
Microsoft's patent describes a system where three separate AI agents split those responsibilities. One agent searches the organization's roster to find whoever (or whatever system) is best positioned to handle the specific threat. A second AI writes the actual fix instructions, drawing on past incidents for guidance. A third agent watches the repair in progress and, if nothing improves, escalates automatically.
The key word is automatically. The system is designed to keep things moving even when the first responder drops the ball, without waiting for a human to notice the silence.
a candidate search agent that: receives information related to a first with respect to a computing resource of a computing network, access candidate data identifying candidates associated with the computing network, and selects a first candidate from the candidate data for remediating the first security event …
Translation: The first AI agent looks at a security problem and chooses who should fix it.
How the three agents hand off tasks and catch failures
The patent lays out a task assignment system built around three distinct AI agents, each with a narrow job.
- Candidate search agent: When a security event is detected on a network, this agent scans a database of available responders (people, automated scripts, or connected systems) and picks the best match. The selection logic leans on similarity: if a responder previously handled a threat that looks like this one, they move to the top of the list.
- Remediation agent: This agent is a generative AI model (the type of AI that produces new text or instructions, similar to how a large language model writes prose) trained specifically on past security tasks. It generates a concrete set of fix instructions tailored to both the threat and the chosen responder, then formally assigns that task.
- Monitoring agent: This agent watches whether the assigned responder actually completes the fix. If they fail or don't respond in time, the monitoring agent triggers a mitigation step, meaning the system escalates or takes a backup action rather than just waiting.
The architecture is explicitly multi-agent, meaning each AI operates independently with its own scope. That separation is deliberate: no single model has to juggle threat analysis, task writing, and progress tracking all at once.
A third AI agent monitors performance of the remediation task and detects if the selected candidate fails to remediate the security event.
Translation: The final AI agent watches the fix happen and catches any failures.
What automated threat response means for IT teams
For IT and security teams, the appeal is coverage. Threats don't stop arriving at the end of a shift, and analysts can't be everywhere. A system that autonomously picks the right responder, writes coherent instructions, and escalates failures closes the gap between detection and containment without requiring a human in the loop for every step.
Microsoft's track record in AI-security patents suggests this is part of a broader effort to fold AI into the Microsoft Defender and Sentinel product lines. For organizations already using those tools, a system like this could shorten the window between "threat spotted" and "threat contained," which is often where the real damage happens.
Microsoft's 31st filing we've tracked since May in our AI models working in teams continues a pattern of self-checking agents, following security agent with built-in critic and self-auditing automation filing.
Source: US 2026/0303618 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 12 sheets
12 drawing sheets from US 2026/0303618 A1 · click any drawing to enlarge


Show the other 4 sheets


More from Microsoft
All 646 Microsoft patents →
More in Security
All 341 Security patents →
IBM
IBM Patents an AI System That Diagnoses and Fixes IT Outages Automatically
Samsung
Samsung Patents an AI System That Reads Security Alerts and Checks Every Device Automatically
IBM
IBM Patent: AI Assistant Actions Are Automatically Screened for Security Threats
Amazon
No comments yet