

IBM
IBM · Security · Filed Jan 2, 2025 · USPTO published Jul 2, 2026 · Jul 2 release
IBM Patents a Login System That Authenticates You by Your Daily Habits
What if your password was replaced by the way you move through your day? IBM is patenting a system that learns your personal routine and uses it as a continuous authentication check.
- Publication number
- US 2026/0187208 A1(US20260187208A1)
- Applicant
- International Business Machines Corporation
- Filed · Published
- Jan 2, 2025 · Jul 2, 2026
- Inventors
- Loucas Loumakos, Adithi Thumballi Ganapathi, Meenakshi Kumari, Ravithej Chikkala, Justin Bonyoma
- Status when we published
- Waiting for an examiner
- Document
- 20 claims
- US classification
- 726/5
- Examiner
- AHSAN, SYED M (Art Unit 2491)
How IBM's behavior-pattern login system works
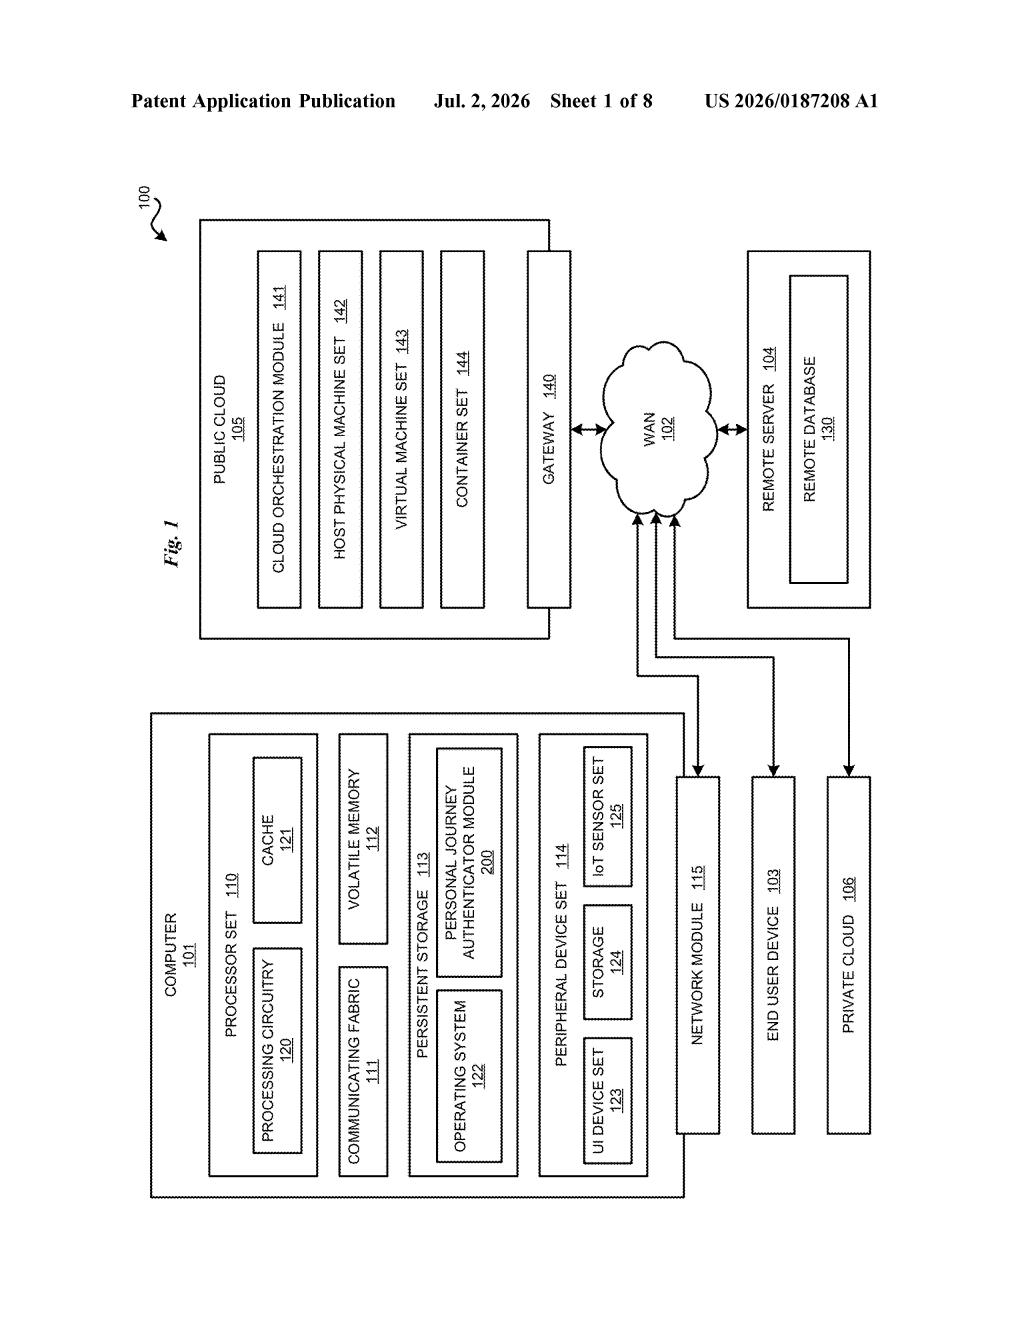
Imagine a security system that watches how you typically use a space or application over time, say which apps you open first thing in the morning, in what order you check your messages, or how you navigate a building. Over time, it builds a picture of your normal routine.
Now imagine that same system checking whether your current behavior matches that learned routine. If something looks off, it can flag the account, lock a door, or ask you to verify your identity. No password required, and no single login moment to steal.
That's the idea behind this IBM filing. Rather than relying on a token or a code you enter once, the system treats your personal pattern of behavior as the credential itself. A mismatch between what you usually do and what's happening right now becomes the trigger for a security response.
How the system builds and compares event sequences
The patent describes a two-phase process. In the first phase, the system runs a data collection process that records how a user interacts within a defined "space," which could be a physical location tracked by sensors, a software environment, or a combination of both. From that raw data, it extracts discrete events and stitches them into a personal journey: an ordered sequence that represents the user's typical behavior pattern.
In the second phase, triggered by some condition (like a login attempt, an access request, or an unusual activity flag), the system collects a fresh batch of behavioral data. It then does two things in parallel:
- Generates a predicted sequence based on what the user's learned pattern says should happen next
- Generates an actual sequence from the newly observed behavior
Those two sequences are compared using a similarity metric (essentially a numerical score measuring how closely the real behavior matches the prediction). If the score falls below a set threshold, the system initiates a "responsive action," which could mean denying access, requiring additional verification, or sending an alert.
The approach is sometimes called continuous authentication because the check is ongoing rather than a single gate at login.
What this means for passwordless and passive security
Passwords are a single point of failure. Steal one credential and you're in. Behavioral authentication is harder to steal because it's not a static secret; it's a pattern that exists only in how a real person moves through their day. For enterprises managing access to sensitive systems, a system like this could catch an attacker who has valid credentials but is behaving nothing like the person those credentials belong to.
For everyday users, the appeal is a world where you never consciously log in at all. The tradeoff is privacy: building this kind of profile means collecting and storing a detailed record of your behavior over time. How IBM handles data minimization and user consent in any real implementation would be the key question.
Source: US 2026/0187208 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time IBM patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
More from IBM
All 470 IBM patents →
More in Security
All 341 Security patents →
Microsoft
Microsoft Patents a Login System That Picks the Right Security Test for Each User
Samsung
Samsung Patents a Way to Stop Login Tokens from Oversharing Your Personal Data

Samsung
Samsung Patents a Chip-Tied Authentication Key System for Secure Storage
Microsoft