
IBM
IBM · Security · Filed May 7, 2025 · USPTO published Nov 12, 2026 · This week's release
IBM Files Patent for Turning Plain-English Requests Into Security Alert Rules
Ask a security tool to "find processes that changed the hosts file often" and it has to guess what "often" means. IBM's filing describes a way to make it look things up, ask questions and check itself before it writes the rule.
- Publication number
- US 2026/0359577 A1(US20260359577A1)
- Applicant
- International Business Machines Corporation
- Filed · Published
- May 7, 2025 · Nov 12, 2026
- Inventors
- Teryl Paul TAYLOR, Shriti PRIYA, Frederico ARAUJO, Ian Michael MOLLOY
- Status when we published
- Waiting for an examiner
- Document
- 20 claims
- US classification
- 704/9
- Examiner
- HUTCHESON, CODY DOUGLAS (Art Unit 2659)
What IBM's plain-English rule writer actually does
Right now, turning a security worry into an alert rule usually means someone writing it by hand in a specialized code language. Typing a plain request like "find processes that changed the hosts file fewer than 10 times" leaves a lot unanswered. What counts as "few"? Over what time period? Which operating system? Does "changed" mean edited or deleted?
IBM's patent application describes a tool that takes that sentence and first boils it down to three pieces: who is doing something, what they are doing it to, and what they are doing. Then it fills in the gaps, such as which file location "hosts file" points to on a given machine, and it can ask you follow-up questions when something is still unclear.
Only after that does it write the finished detection rule, the set of conditions security software watches for. The filing says hand-writing these rules is slow and easy to get wrong, and this is its answer.
… converting the natural language prompt into an intermediate representation comprising a subject, an object, and an action; disambiguating the subject, the object, and the action in the intermediate representation to form a disambiguated intermediate representation; …
Translation: The system breaks down a plain-English request into its core parts and clarifies any vague terms.
How the request gets pinned to who, what and action
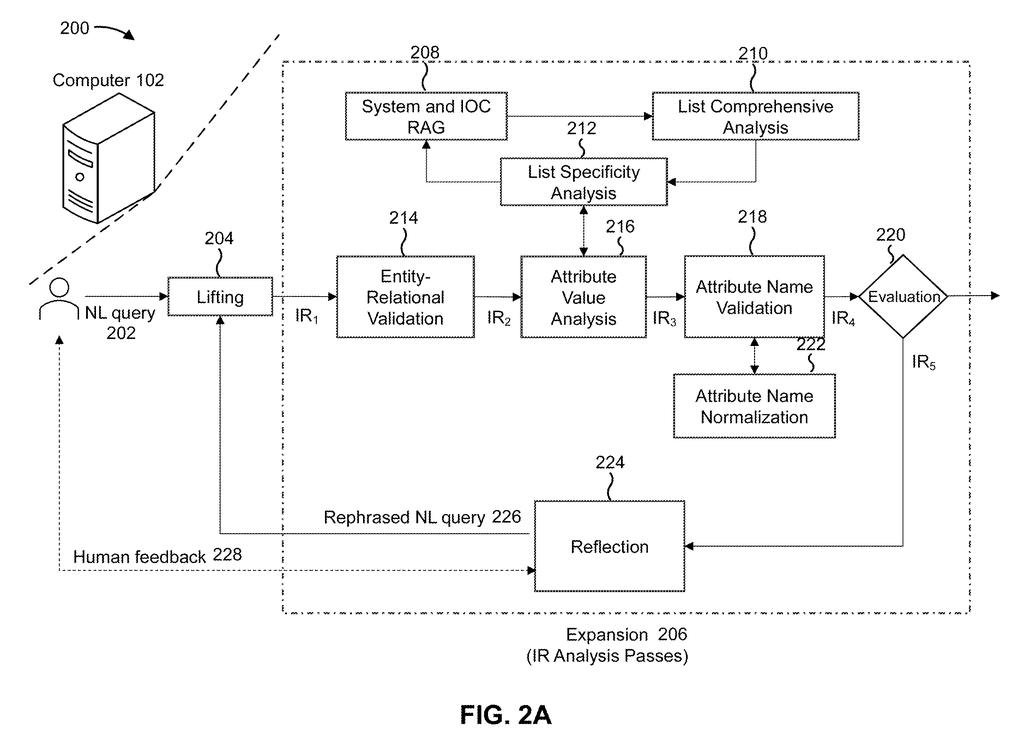
The filing describes a pipeline with four stages. A large language model (LLM, the AI behind chatbots) first "lifts" the typed request into an intermediate representation, a structured stand-in with a subject, an object and an action. In the filing's example, "process" is the subject, "file" is the object and "changed" is the action.
- Disambiguate: check the three parts for conflicts. A process can only read, write, create or delete a file, so other verbs get flagged. Attribute names are matched against a predefined list, because LLMs can invent names.
- Enrich: use retrieval augmented generation (RAG, which looks up relevant facts in a knowledge base) and threat intelligence feeds to swap vague terms for specifics, such as turning "hosts file" into its real file paths.
- Validate: score the draft on things like attribute matching and feasibility. If it fails, the system can rephrase the request, ask the user, or loop again until accuracy is high enough.
- Synthesize: write the rule in a format such as Sigma, Kusto or an XDR query language (XDR is a broad security-monitoring system), with a conversion tool for moving between them.
The output can come with a written explanation of why the rule looks the way it does, and the whole thing can sit behind a simple input screen.
The device may enrich the disambiguated intermediate representation with relevant information to form an enriched intermediate representation.
Translation: The software adds necessary security context to make the parsed request useful for monitoring.
Why checking the AI's work matters to security teams
If you work on a security team, the pitch is simple: describe a threat in a sentence and get a rule your monitoring software can run, instead of writing it in a specialized query language. The filing frames hand-built rules as slow and error-prone, and faster rule creation is the payoff. It also lists lower processing and memory use as a side benefit.
The more interesting part is the guardrails. AI models can make up details, so the design boxes the request into three slots, checks names against a fixed list, and scores the draft before anything is written. If you have ever watched a chatbot confidently invent a fact, you can see why a security team would want that. The filing does not name a product it would ship in.
IBM's 79th patent application we've tracked since May in the AI guardrails race adds to a thread that includes a panel of AI judges and a memory system for long texts.
Source: US 2026/0359577 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time IBM patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 8 sheets
8 drawing sheets from US 2026/0359577 A1 · click any drawing to enlarge


More from IBM
All 470 IBM patents →
More in Security
All 341 Security patents →
Salesforce
Salesforce Patents a Background Check on the AI Helpers It Sends to Do Your Work
OpenAI
OpenAI Patents an AI Bug Hunter That Tests Its Own Findings Before Reporting Them
Microsoft
Microsoft Files Patent for AI Coding Help That Checks Its Own Work First
Nvidia
No comments yet