
Microsoft
Microsoft · Security · Filed Mar 31, 2025 · USPTO published Oct 1, 2026 · Oct 1 release
Microsoft Patents a Crowdsourced System That Auto-Blocks Dangerous Files Across Companies
What if every company's malware encounter could instantly protect every other company? That is the core idea behind Microsoft's latest security patent, which describes a system that pools threat reports from thousands of organizations and automatically blocks dangerous files before they can run.
- Publication number
- US 2026/0300487 A1(US20260300487A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Mar 31, 2025 · Oct 1, 2026
- Inventors
- Yaakov GARYANI, Roi Tzadok
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 713/164
- Examiner
- KNACKSTEDT, JACOB BENEDICT (Art Unit 2408)
How Microsoft's threat-pooling file-blocking actually works
You're an IT admin, and a nasty piece of software just hit one of your company's computers. Your security team flags it, but meanwhile the same file is sitting dormant on machines at hundreds of other businesses. By the time anyone else reacts, the damage is done.
Microsoft's new patent describes a way to fix that delay. When your security system marks a file as dangerous, that report gets pooled with reports from every other company using the same service. The more independent organizations flag the same file, and the faster those flags pile up, the higher the file's risk score climbs. Once the score crosses a set threshold, the system automatically pushes a block order to all participating companies' computers, stopping the file from running.
The score also weighs who is doing the reporting. Organizations with strong security track records carry more weight than newcomers, which helps filter out false alarms. Blocking can happen remotely or directly on the device, and what level of protection you get depends on your subscription tier.
… assigning a risk score to each file, wherein the risk score is dynamically adjusted based on at least one of: a volume of independent organizations classifying the file as malicious, respective reputations of the organizations providing classifications, or a temporal distribution of classifications over time …
Translation: The system calculates a risk score using factors like how many companies flagged the file, who reported it, and when.
How the risk score is built and when blocking kicks in
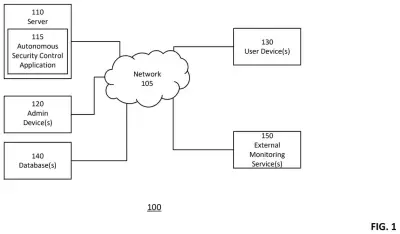
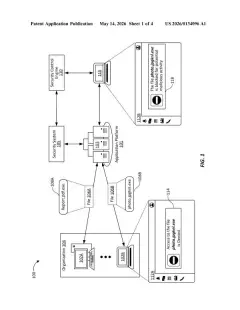
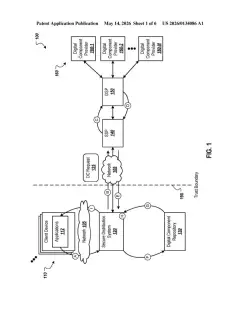
The patent describes a cloud-based security service that aggregates incident classification data from many organizations simultaneously. Each organization's security software can tag a file as malicious and send a report back to a central system, including a file identifier and the risk classification.
The central system then builds a risk profile for each file using three main signals:
- Volume: how many independent organizations have flagged the file
- Source reputation: how trustworthy the flagging organizations are, based on their historical accuracy
- Temporal distribution: how the reports are spread over time (a sudden spike in flags carries more urgency than a slow trickle)
When the composite risk score crosses a predefined threshold, the system automatically generates an execution prevention policy, essentially a binding instruction that tells every subscribed device to refuse to run that file. That policy is then pushed out to all participating organizations' computers.
Prevention can happen at two points: the central service can block the file remotely before it ever reaches a device, or the policy can be enforced locally on the device itself. The patent notes that the level of response can vary by subscription level and by the type of threat, suggesting a tiered commercial model is built into the design.
If the score exceeds a threshold, an execution prevention policy is generated and transmitted to devices for enforcement.
Translation: When a file is deemed too dangerous, the system creates a rule to block it on connected computers.
What this means for business security software
For businesses, the gap between a file being first spotted as dangerous and every computer being protected against it is where breaches happen. A system that compresses that window from hours (or days) to minutes by automating the entire response chain addresses one of the most persistent problems in enterprise security.
the pattern in Microsoft's enterprise security filings points toward tighter integration between its cloud services and the devices businesses already run. For organizations using Microsoft's security products, this kind of system could mean less reliance on individual IT teams catching threats manually and more protection that runs in the background, though the tiered subscription structure also signals that the best protection would likely come at a premium.
Microsoft's 483rd filing in our Microsoft coverage since May continues a run of security-focused applications, following one on shielding data during AI use and one on checking software safety before it runs.
Source: US 2026/0300487 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 3 sheets
3 drawing sheets from US 2026/0300487 A1 · click any drawing to enlarge


More from Microsoft
All 646 Microsoft patents →
More in Security
All 341 Security patents →
Qualcomm
Qualcomm Patents a System to Authenticate 5G Network Broadcasts Before Your Device Trusts Them
Google
Google Patents a System That Grabs Abandoned Domains Before Hackers Can
Adobe
Adobe Patents a Password System That Uses Keystroke Timing as a Security Factor
Google
No comments yet