
Microsoft
Microsoft · Security · Filed Mar 28, 2025 · USPTO published Oct 1, 2026 · Oct 1 release
Microsoft Patents a Cloud Security System That Finds Sensitive Data Before Attackers Do
Most security tools wait for something to break before raising an alarm. Microsoft's new patent describes a system that continuously maps every resource in a cloud environment, figures out which ones are sensitive, and watches for suspicious behavior before any breach occurs.
- Publication number
- US 2026/0303628 A1(US20260303628A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Mar 28, 2025 · Oct 1, 2026
- Inventors
- Abhijeet Surendra HATEKAR, Harish SANGIREDDY, Wesley Scott DRONE
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 726/23
- Examiner
- TRAORE, FATOUMATA (Art Unit 2436)
What Microsoft's cloud security graph actually does
Every time a company's cloud system gets a new database, storage bucket, or application, a security team somewhere has to decide: is this thing important enough to watch closely? That question gets harder as cloud environments grow to thousands of connected pieces.
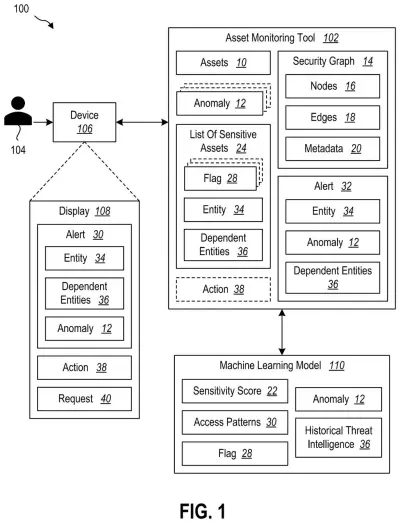
Microsoft's patent describes software that answers that question automatically. It builds a kind of relationship map of everything running in a cloud environment, then uses an AI model to figure out which resources are sensitive on their own and which nearby resources become sensitive by association. A billing database might be obviously important, but so is the logging tool that can read it.
Once the system has its list, it watches how people and programs interact with those resources. If something looks off, such as access at an unusual hour or from an unexpected account, it sends an alert. The goal is to surface threats early, not after damage is done.
traversing, using a machine learning model, a security graph with nodes representing entities in a cloud environment and edges representing relationships between the entities …
Translation: An AI maps out everything in the cloud and how those pieces connect to each other.
How the system maps assets and spots suspicious access
The system builds a security graph, a data structure where every entity in a cloud environment (users, services, databases, storage, virtual machines) is a node, and every relationship between them is an edge. Think of it like a wiring diagram for a whole company's cloud.
A machine learning model traverses that graph, reading metadata attached to each node (things like resource type, owner, compliance tags, and access permissions) to decide which entities qualify as sensitive assets. Crucially, the model then follows the graph's edges to find dependent entities, resources that aren't obviously sensitive themselves but are closely connected to ones that are. Those dependents get added to the watch list too.
Once the sensitive asset list is built, the system continuously monitors access patterns for everything on it. When the model detects an anomaly (a pattern that deviates from established behavior), it fires an alert.
Key components:
- A graph database enriched with resource metadata
- An ML model that both classifies sensitivity and discovers indirect dependencies
- A continuous access-pattern monitor tied to the sensitive asset list
- An automated alerting layer triggered by anomaly detection
The present disclosure relates to systems and methods for identifying cybersecurity risks. The systems and methods automate monitoring and anomaly detection.
Translation: This patent covers automated tools that watch for unusual activity to spot security threats.
What this means for businesses running cloud infrastructure
For businesses running workloads on cloud platforms like Azure, the hardest part of security is often knowing what to protect. Cloud environments change constantly, and a resource that looked low-risk last month might become a critical data path today. A system that re-evaluates sensitivity automatically, and extends that evaluation to dependent resources, removes a category of blind spots that human teams routinely miss.
Microsoft keeps filing around cloud-native security automation, and this patent fits that pattern. For IT buyers and security teams, the practical promise is fewer manual audits and faster detection of the lateral-movement attacks, where an intruder moves from a low-value entry point to a sensitive target, that are behind most major breaches.
Microsoft's 455th filing in our Microsoft coverage since May follows work on cloud threat mapping and split-processor video quality.
Source: US 2026/0303628 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 5 sheets
5 drawing sheets from US 2026/0303628 A1 · click any drawing to enlarge


More from Microsoft
All 646 Microsoft patents →
More in Security
All 341 Security patents →
IBM
IBM Patents a System That Automatically Finds Sensitive Data Hiding in Databases
IBM
IBM Patents an AI System That Rewrites Data Security Rules During Live Collaboration
Microsoft
Microsoft Patents a Security Filing That Only Lets Verified Senders Pass Data Through
Microsoft
No comments yet