
Google
Google · Security · Filed Jun 10, 2026 · USPTO published Oct 1, 2026 · Oct 1 release
Google Patents a Method for Picking Ads Without Seeing Your Personal Data
Every time an ad loads on your screen, several systems have already negotiated what to show you. Google's new patent describes a way to run that negotiation inside locked, tamper-proof computing environments so your personal data never has to leave a protected space to do it.
- Publication number
- US 2026/0300471 A1(US20260300471A1)
- Applicant
- Google LLC
- Filed · Published
- Jun 10, 2026 · Oct 1, 2026
- Inventors
- Akhil Dhavala, Shruti Murali, Hari Krishna Bikmal, Michael Feng, Oscar Ka Ho Chow, Ouyang Zhang, Jacob Mark Hallberg
- Status when we published
- Waiting for an examiner
- Document
- 20 claims
- US classification
- 726/26
- Parent application
- Continuation of 18/860,186 (filed Oct 25, 2024)(18860186)
How Google serves ads without handing over what it knows about you
Every time a web page loads an ad, a small auction happens in milliseconds. Servers decide which ad to show you based on who you are, what you've browsed, and what advertisers are willing to pay. Normally, all of that context travels between systems, and your data gets exposed along the way.
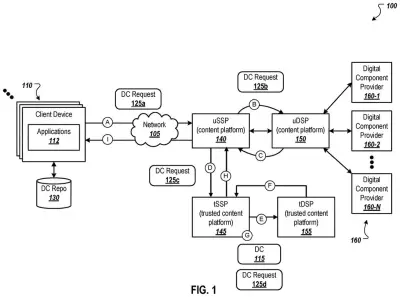
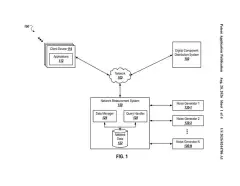
Google's patent describes splitting that process between two separate "trusted" computing environments. Think of each one as a locked room with strict rules about what can go in and what can come out. One room picks ads based on the context of the page you're visiting. The other picks ads that are tied to your personal profile but only sends back a number, not your actual data.
The two rooms then combine those numbers to decide which ad you see. At no point does either room hand raw personal information to the other. Google calls these locked rooms trusted execution environments, and the goal is to let ad targeting work while keeping the underlying data confined.
… providing, to one or more second untrusted content platforms, a second digital component request comprising the contextual data, wherein the encrypted user data is excluded from the second digital component request; …
Translation: Ad networks share the context of the page without passing along your personal identity.
How the two trusted platforms split the selection work
The patent describes a system with two trusted content platforms (CPs), each running inside a trusted execution environment (TEE). A TEE is a cordoned-off section of a processor that even the operating system cannot inspect; code running inside it is isolated from everything else on the machine.
The first trusted CP receives a bundle of ad candidates. That bundle contains two types:
- Constrained digital components (DCs): ads tied to user-specific data, like interest categories, along with rules about how they can be selected (the "distribution parameters").
- Contextual DCs: ads chosen purely based on the content of the page being loaded, with no personal data involved.
The first CP forwards the constrained ads and their rules to the second trusted CP. The second CP does the personalized selection work and sends back only selection values, numerical scores, rather than the underlying user data that produced them. It also sends back a set of constraining values that cap or shape what the first CP can do next.
The first CP then compares those scores against scores for the contextual ads and picks the winner. Because each environment is isolated and only numeric outputs cross the boundary between them, neither system needs to share raw personal data with the other.
Methods, systems, and apparatus, including medium-encoded computer program products for selecting and displaying content in privacy preserving manners are described.
Translation: Google patented a system for picking and showing ads while keeping user data private.
What this means for privacy in targeted advertising
For you as a reader, this is mostly invisible in normal browsing. You would not notice a different ad or a faster page load. Where you might notice it is in the absence of something going wrong: this kind of architecture is designed to prevent the kind of data leakage that happens when ad systems pass personal information across insecure channels.
Google's long bet on privacy-preserving ad infrastructure shows up repeatedly in its engineering filings. Whether this specific approach makes a practical difference depends on how widely TEE-based ad selection gets deployed and whether the rest of the ad supply chain adopts compatible standards. The patent protects the architecture; the impact depends on adoption.
Google's 54th filing we've tracked since May in our on-device AI privacy watchlist follows its applications for asking before sharing data and user-controlled ad spaces.
Source: US 2026/0300471 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Google patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 4 sheets
4 drawing sheets from US 2026/0300471 A1 · click any drawing to enlarge


More from Google
All 1,127 Google patents →
More in Security
All 353 Security patents →
Microsoft
Microsoft Patents a Way to Send Your Voice to AI Without Exposing Who You Are
Apple
Apple Patents a System That Tracks Who Looked at Your Health Records
Apple
Apple Patents a Way to Keep Your Private Data Off Shared Devices
Microsoft
No comments yet