
IBM
IBM · Networking · Filed Feb 21, 2025 · USPTO published Aug 13, 2026 · Aug 13 release
IBM Patents a Way to Shrink Encrypted Data Before Sending It
Encryption and compression normally can't work together because encrypted data looks like random noise. IBM's new patent describes a clever workaround that does both, in the right order.
- Publication number
- US 2026/0238476 A1(US20260238476A1)
- Applicant
- INTERNATIONAL BUSINESS MACHINES CORPORATION
- Filed · Published
- Feb 21, 2025 · Aug 13, 2026
- Inventors
- Oliver Benke, Tobias Ulrich Bergmann, Matthias Ringe
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 713/168
- Examiner
- SALEHI, HELAI (Art Unit 2433)
How IBM squeezes encrypted data before it travels
Every time a server sends encrypted data across a network, it ships a full, bloated package that nobody has bothered to shrink first. That's because encryption scrambles data so thoroughly that standard compression tools can't find the repetitive patterns they need to do their job.
IBM's patent proposes solving this with a carefully sequenced process: briefly decrypt the outgoing data, compress it using a shared "dictionary" that both the sender and receiver already know, then encrypt it again before it ever leaves the building. The result is a smaller, still-secure package.
The key piece is that shared static compression dictionary. Both computers agree on it in advance, so the receiver can decompress without needing any extra information sent along with the data. You get the size savings without sacrificing the security you started with.
… compressing the decrypted data stream using a predefined static compression dictionary shared with a recipient computer system; …
Translation: It shrinks the unencrypted data using a shared dictionary known to both sender and receiver.
Inside IBM's decrypt-compress-encrypt pipeline
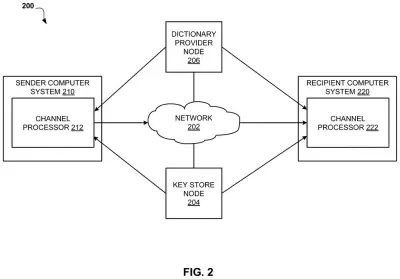
The patent describes a process handled by a channel processor, a dedicated component inside the sender's computer system that manages the flow of outgoing data.
The sequence works like this:
- The channel processor receives an already-encrypted outgoing data stream.
- It triggers decryption of that stream, briefly exposing the raw data internally.
- It compresses the decrypted data using a predefined static compression dictionary (a fixed lookup table of common patterns, agreed upon ahead of time with the recipient, rather than built on the fly from the data itself).
- It triggers re-encryption of the compressed result.
- It hands the final encrypted, compressed stream off to the network for transmission.
The critical design choice is the static dictionary. Normal compression algorithms scan the data they're working on to build their own internal reference tables, which is exactly what you can't do with encrypted content. A pre-shared static dictionary sidesteps that problem entirely because the compression rules are established before the data ever arrives.
The recipient, holding the same dictionary, can reverse the process: decrypt, then decompress, restoring the original data.
According to embodiments, a method, computer system, and computer program product for handing over an encrypted outgoing data stream by a sender computer system is provided.
Translation: The patent describes a system designed to process and transmit encrypted data securely.
What this means for enterprise data transfer costs
For large enterprise systems, especially mainframe environments where IBM dominates, moving encrypted data at scale is expensive. Bandwidth costs money, and network throughput is a real bottleneck. A reliable way to compress encrypted traffic without weakening security could meaningfully reduce both costs and transmission times for organizations that send large volumes of sensitive data, like financial records or health data, continuously across private networks.
The practical scope here is narrower than it might first appear. The approach works best in controlled, pre-arranged connections where both sides can share a static dictionary in advance, which suits IBM's enterprise and mainframe customer base well. This kind of encryption-layer efficiency work sits alongside a steady stream of new Big Tech patents targeting data-center infrastructure, where incremental gains in throughput and cost add up quickly at scale.
Source: US 2026/0238476 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time IBM patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 3 sheets
3 drawing sheets from US 2026/0238476 A1 · click any drawing to enlarge


More from IBM
All 470 IBM patents →
More in Networking
All 498 Networking patents →
Qualcomm
Qualcomm Patents a Way to Give Networks a Peek Inside Encrypted Traffic
Qualcomm
Qualcomm Patents a Way for Wi-Fi Routers to Identify Which App Is Sending Your Data
Microsoft
Microsoft Patents a Way to Send Datacenter Data Through Flashing Light Patterns
Sony