
AMD
AMD · Security · Filed Jan 29, 2025 · USPTO published Jul 30, 2026 · Jul 30 release
AMD Patents an Internal Security Check for Network Chips That Blocks Unauthorized Access
AMD has filed a patent for a method that puts a security gatekeeper inside the network chip itself, so that even traffic that gets onto the card can't access parts of it that it shouldn't.
- Publication number
- US 2026/0220255 A1(US20260220255A1)
- Applicant
- Advanced Micro Devices, Inc.
- Filed · Published
- Jan 29, 2025 · Jul 30, 2026
- Inventors
- Sameer KITTUR SUBRAHMANYA, Krishna DODDAPANENI, Murty Subbaramachandra KOTHA, Neel PATEL, James Bradley SMITH, Shrikant VAIDYA
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 726/23
- Examiner
- TRAN, ELLEN C (Art Unit 2433)
What AMD's network chip lockdown actually does
Imagine your office building lets anyone through the front door, but then requires a separate badge scan before you can enter any individual room. AMD is applying that idea to the chips that connect computers to a network.
A network interface controller (NIC) is the hardware inside a server or PC that handles all incoming and outgoing network traffic. Right now, if something malicious gets far enough into that chip, it may be able to reach resources it was never meant to touch. AMD's patent describes a system where every internal request, called a transaction, is checked against both what it's asking for and what rules apply to the target it's trying to reach.
Only transactions that pass that internal check are actually allowed through. Ones that don't are blocked before they can do any damage.
How the controller checks each transaction before passing it through
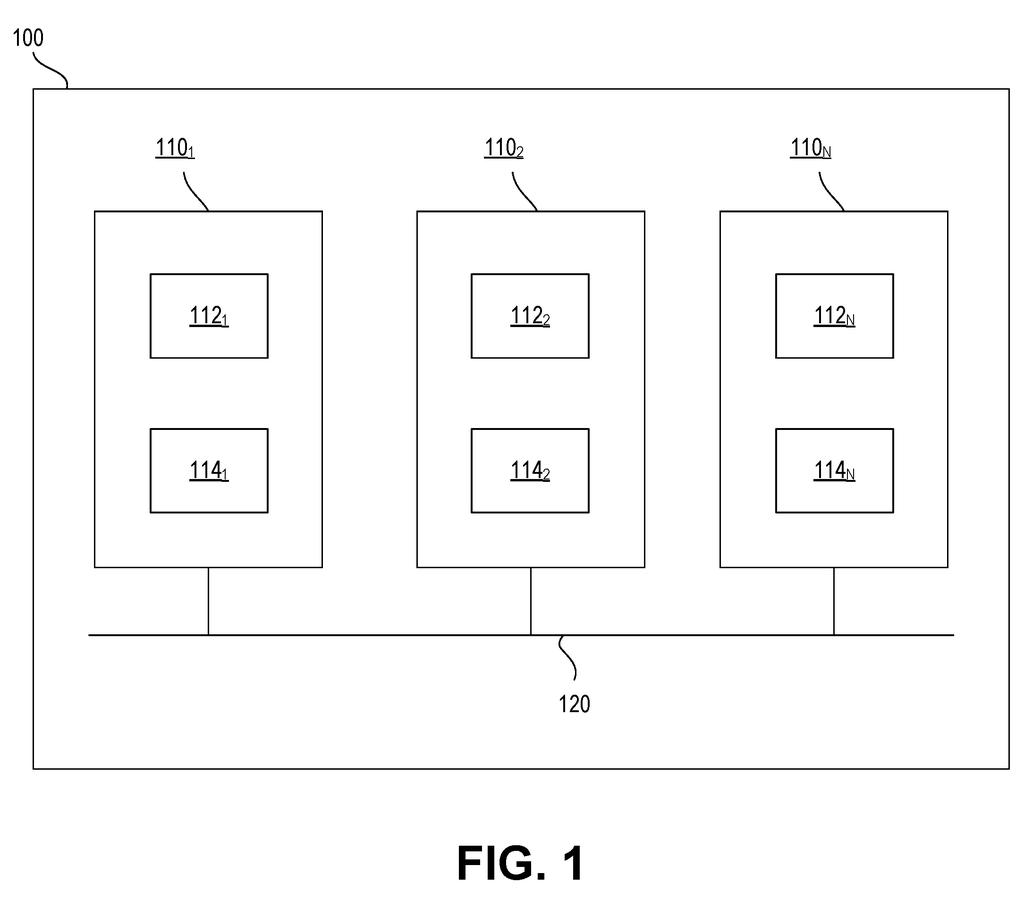
The patent describes a method where the network interface controller (NIC) itself acts as an internal traffic cop, not just a pass-through device.
When any transaction (a request to read from or write to a resource inside the NIC) arrives, the controller evaluates two things:
- A characteristic of the transaction itself, such as who or what is initiating it and what permissions it carries.
- A characteristic of the target resource inside the NIC, such as what access rules that specific resource has defined.
Only if those two characteristics line up correctly does the controller forward the transaction to its destination. Otherwise, it's blocked. The patent calls this isolation of functions, meaning different parts of the NIC are separated so one compromised function can't reach another.
This is essentially access control (the same idea behind user permissions on an operating system) applied at the hardware level inside a network chip, rather than relying entirely on software running above it.
What this means for server and data-center security
Data centers are full of NICs handling enormous volumes of traffic, and attackers increasingly target hardware-level components because a compromise there can sit below the operating system and be very hard to detect. Putting access control inside the NIC means a rogue driver, a compromised virtual machine, or a malicious peripheral can't freely reach all the chip's internal resources even if it gets a foothold on the card itself.
For AMD, which sells network and compute silicon into cloud providers and enterprise data centers, this kind of isolation is a selling point for customers who need to demonstrate strong hardware security. It also fits into broader industry trends around confidential computing and hardware root-of-trust, where security guarantees are pushed as close to the silicon as possible.
Source: US 2026/0220255 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time AMD patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 5 sheets
5 drawing sheets from US 2026/0220255 A1 · click any drawing to enlarge


More from AMD
All 119 AMD patents →

More in Security
All 341 Security patents →
Microsoft
Microsoft Patents a System That Blocks Devices From Reaching Corporate Authentication Servers
Samsung
Samsung Patents a System That Controls 5G Network Access Based on User Permissions
Microsoft
Microsoft Patents a Security Filing That Only Lets Verified Senders Pass Data Through

IBM