
IBM
IBM · Security · Filed Feb 4, 2025 · USPTO published Aug 6, 2026 · Aug 6 release
IBM Patents a Way to Find Security Leaks Hidden in a Chip's Power Draw
Your computer's chip might be broadcasting your secrets through nothing more than how much electricity it consumes at any given moment. IBM has filed a patent for a system that hunts down exactly those kinds of leaks before a chip ever leaves the design stage.
- Publication number
- US 2026/0227961 A1(US20260227961A1)
- Applicant
- International Business Machines Corporation
- Filed · Published
- Feb 4, 2025 · Aug 6, 2026
- Inventors
- Naorin Hossain, Ramon Bertran Monfort, William Santiago-Fernandez, Alper Buyuktosunoglu, Pradip Bose
- Status when we published
- Waiting for an examiner
- Document
- 25 claims
- US classification
- 717/106
How IBM spots secrets leaking through chip power use
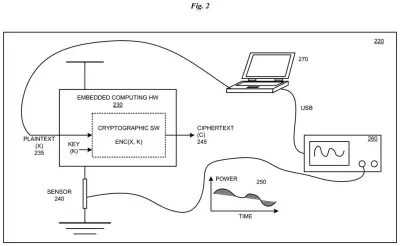
Imagine a safe that, every time you open it, flickers a light proportional to how many digits are in your combination. You haven't told anyone the code, but an attacker watching the light could eventually figure it out. Computer chips have the same problem: they consume slightly different amounts of power depending on what data they're processing, and attackers can exploit that pattern to reconstruct sensitive information like encryption keys.
IBM's patent describes a tool that simulates how a chip will behave during design, models the exact power consumption of individual instructions, and generates test code to verify whether those patterns could leak anything useful to a spy. The goal is to catch the problem before the chip is manufactured, not after.
If the system finds a leak, engineers can adjust the chip's design, both at the high-level architecture and the finer microarchitecture level, to mask the tell-tale power signals. Think of it as proofreading a chip's behavior for accidental confessions.
determining a power consumption result of a hardware representative system comprising: constructing a power consumption relation based in part on an instruction; and generating executable code based on the power consumption relation …
Translation: The system figures out how much power a chip design uses by writing code that simulates specific instructions.
How IBM models power draw to expose vulnerable instructions
The patent describes a three-step pipeline for identifying and eliminating power side-channel vulnerabilities (places where a chip's electricity consumption patterns inadvertently reveal the data it's working on).
- Model construction: The system builds a mathematical "power consumption relation" for individual chip instructions. This is essentially a formula that predicts how much power a given instruction will draw depending on what data it is operating on.
- Executable code generation: Using that model, the system automatically generates runnable test code. Executing that code produces a concrete power trace (a time-stamped log of power readings) that represents what an adversary could observe from the outside.
- Architecture adjustment: The system computes a power leakage metric (a score measuring how much useful information leaks through the power trace) and feeds that back to engineers, who can then modify both the architecture (the chip's logical design) and the microarchitecture (the lower-level implementation details) to reduce the leak.
The process works on a hardware representative system, meaning a simulation or model of the chip rather than physical silicon, so vulnerabilities can be caught and corrected during design rather than after mass production.
… adjusting an architecture and a microarchitecture of the hardware representative system according to the power leakage metric.
Translation: Engineers then modify the chip layout to patch any security vulnerabilities found in the power signals.
What this means for chip security before hardware ships
Power side-channel attacks are a real and documented threat. Attacks like TEMPEST and various differential power analysis techniques have been used to extract cryptographic keys from physical devices. The challenge is that fixing these problems after a chip is manufactured is extremely expensive, and often impossible without a full redesign. A tool that finds them at the design stage could save significant cost and prevent security patches that never fully close the gap.
For you, this is most relevant if you rely on hardware security for things like encrypted storage, financial transactions, or enterprise data protection. If this kind of tooling becomes standard practice in chip design, the hardware underneath your security software gets meaningfully harder to spy on.
Source: US 2026/0227961 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time IBM patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 8 sheets
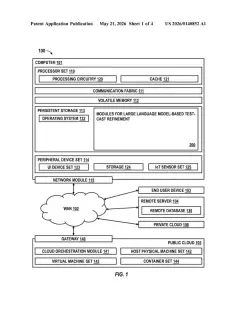
8 drawing sheets from US 2026/0227961 A1 · click any drawing to enlarge


More from IBM
All 470 IBM patents →
More in Security
All 341 Security patents →
Qualcomm
Qualcomm Patents a Two-Layer Biometric System That Splits Your Fingerprint Data Across Isolated Chip Zones
Qualcomm
Qualcomm Patents a Chip That Tightens Its Own Security When It Overheats
Intel
Intel Patents Technology to Reconfigure Its Security Hardware During Operation
IBM