
Microsoft
Microsoft · Security · Filed Mar 28, 2025 · USPTO published Oct 1, 2026 · Oct 1 release
Microsoft Patents an AI System That Tracks Online Behavior to Detect Cyberattacks
Every time something happens in a cloud system, Microsoft's patented approach gives that event a unique digital fingerprint, so anything that looks even slightly off gets flagged automatically.
- Publication number
- US 2026/0303619 A1(US20260303619A1)
- Applicant
- Microsoft Technology Licensing, LLC
- Filed · Published
- Mar 28, 2025 · Oct 1, 2026
- Inventors
- Abhijeet Surendra HATEKAR, Harish SANGIREDDY, Wesley Scott DRONE
- Status when we published
- Examiner raised objections; the company can respond
- Document
- 20 claims
- US classification
- 726/23
- Examiner
- NOAMAN, BASSAM A (Art Unit 2497)
What Microsoft's cloud activity fingerprinting actually does
You're running a company on cloud software, and somewhere in thousands of automated daily actions, a hacker does something they shouldn't. No alarm goes off because the action looks, on the surface, pretty normal.
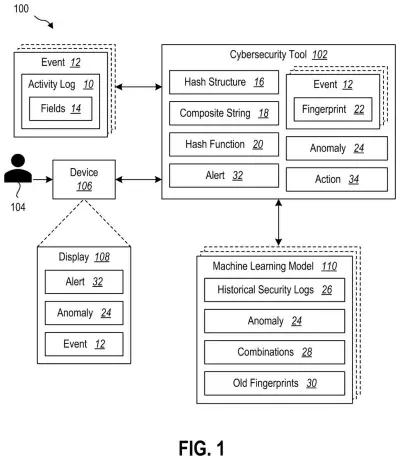
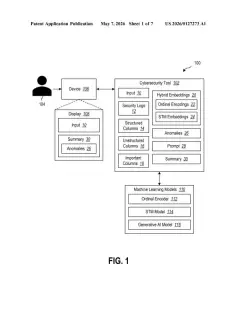
Microsoft's patent describes a system that assigns a unique fingerprint to every event in a cloud environment, like a login, a file access, or a settings change. That fingerprint is generated by feeding details from activity logs into a machine learning model, which compresses them into a short, fixed code. If a later event produces a fingerprint that doesn't match expected patterns, the system flags it as suspicious.
Think of it like a bouncer who has memorized every regular guest's face and handshake. A new combination, even a subtle one, triggers a second look. The goal is to catch threats that would otherwise blend in with normal traffic.
… forming, by the machine learning model, a composite string with the information; applying, by the machine learning model, a hash function to the composite string; generating, by the machine learning model, a fingerprint for the event in response to applying the hash function to the composite string, wherein the fingerprint is a unique value for the event; …
Translation: The system turns log data into a unique ID to track online behavior.
How the hash function builds a unique event fingerprint
The system starts by pulling fields from an activity log (a running record of everything that happens in a cloud environment, like who logged in, from where, and what they touched). A machine learning model extracts relevant pieces of information from those fields and combines them into a single composite string, essentially one long text value that represents all the key details of that event.
That composite string is then run through a hash function (a mathematical process that converts any input into a short, fixed-length code). The result is a fingerprint: a unique value tied to that specific event and its combination of attributes. Because hash functions are deterministic, the same event always produces the same fingerprint, and any change to the underlying details produces a completely different one.
The system then compares fingerprints across events to look for anomalies (patterns that deviate from what's normal). When something unusual is detected, the system triggers an action, which could mean alerting a security team, blocking the activity, or logging it for review.
- Extracts data fields from cloud activity logs
- Builds a composite string from those fields
- Applies a hash function to produce a unique fingerprint
- Flags fingerprints that indicate anomalous behavior
The systems and methods generate a unique fingerprint for an event in the cloud environment using a hash structure. The systems and methods detect an anomaly in the event using the fingerprint.
Translation: Cloud activity is checked for unusual patterns by comparing unique event IDs.
What this means for cloud security and IT teams
For IT and security teams, the promise here is reducing the needle-in-a-haystack problem. Cloud environments generate enormous volumes of log data every day, and manually reviewing it for threats is not realistic. A fingerprint-based approach gives analysts a consistent, machine-readable way to compare events at scale, potentially catching attacks that slowly build over time rather than triggering obvious alarms.
For everyday users, the impact is indirect but real: better cloud security means your data stored in Microsoft 365, Azure, or similar services is harder for attackers to access. The system is designed to catch the subtle intrusions, the ones where a bad actor already has a foothold and is moving carefully.
Microsoft's 457th filing in our Microsoft coverage since May adds to a security thread that includes a self-checking AI agent and a sensitive-data finder.
Source: US 2026/0303619 A1 at the USPTO (PDF). Full patent text and figures are in the official publication.
Get our take in your Top Stories
Liked this breakdown? Add Patentlyze as a preferred source on Google, and our plain-English take shows up more often in your Top Stories the next time Microsoft patent news breaks.
Add Patentlyze on Google
One click.
There are more where this came from
We read every patent application Big Tech publishes and send you the ones worth knowing. Plain English, free, every week.
The drawings · 4 sheets
4 drawing sheets from US 2026/0303619 A1 · click any drawing to enlarge


More from Microsoft
All 646 Microsoft patents →
More in Security
All 341 Security patents →
IBM
IBM Patents a System That Watches for Fake Behavior Inside Virtual Worlds
Samsung
Samsung Patents Technology That Automatically Shields Your Phone From Future Hacker Threats
IBM
Red Hat's New Patent Watches AI Models for Signs of Tampering
Microsoft
No comments yet